Architects Of Trust: Deloitte
Cloud Control: How Deloitte is bringing governance into the region’s AI and digital transformation conversation
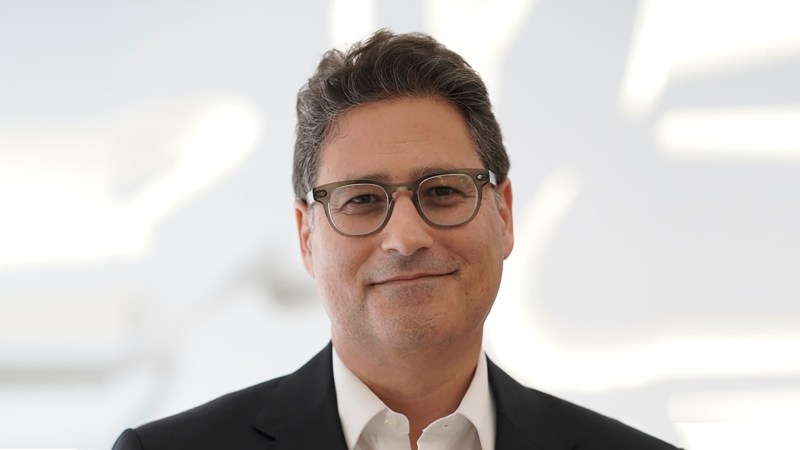
Mutasem Dajani, Deloitte Middle East CEO
You're reading Entrepreneur Middle East, an international franchise of Entrepreneur Media.
Deloitte Middle East, led by CEO Mutasem Dajani, is putting governance on the same agenda as technology and organizational change as AI and cloud systems move into institutional decision-making.
Who controls the data? How can an automated decision be explained? And who has the authority, and the ability, to step in? A public institution moving its services to the cloud has to answer all of these, and the answers extend beyond choosing a platform. Questions like these turn a technology program into an exercise in institutional accountability, which also explains why such programs call for such a broad bench of professional expertise.
That breadth is something Deloitte has been building for a long time. The firm traces its uninterrupted Middle East presence back to 1926, and its regional offering now runs from audit and controls assurance to cyber, engineering, AI and data, alongside risk, regulatory and forensic services. The connection between those disciplines matters: the way a change in systems can alter what an organization needs to oversee, document and test.
The regional business is led by Mutasem Dajani, Deloitte Middle East CEO and a member of the Deloitte EMEA executive committee. Dajani joined Deloitte in 2002, and he previously led its Middle East Audit & Assurance practice and served as UAE Regional Managing Partner. That background is a fitting reference point for an organization whose work spans both introducing change and scrutinizing business information.
Deloitte made the link between technology and institutions explicit at the World Governments Summit in February 2025, where it released two reports. (The summit named the firm its official Knowledge Partner for an 11th consecutive year.) The first, Sovereignty in AI and Cloud, examined data protection, regulatory compliance, algorithmic transparency and ethical standards, alongside the trade-offs between cost, scalability and security.
The second, Driven by Skills: Unlocking the Potential of the Public-Sector Workforce in GCC, looked at a shift toward organizing workforce development around skills. Read together, the two publications make a practical argument: an institution’s capacity to govern new technology depends partly on the capabilities of the people using and supervising it. Technical choices and organizational choices belong in the same discussion.
A control written into a policy has limited value if responsibility is unclear or staff can’t apply it. A digital service can run efficiently and still leave hard questions about access, oversight and accountability unanswered. As such, the quality of any transformation is also a question of how an institution explains and governs its decisions.
That is where Deloitte’s mix of a regional presence dating back to 1926 and a remit spanning systems, risk and people comes in. Its published work pushes the governance questions to the start of the project, while the design of a new service can still make room for the responsibilities that come with it. Ask those questions after launch, and they get much harder to answer.
Deloitte Middle East, led by CEO Mutasem Dajani, is putting governance on the same agenda as technology and organizational change as AI and cloud systems move into institutional decision-making.
Who controls the data? How can an automated decision be explained? And who has the authority, and the ability, to step in? A public institution moving its services to the cloud has to answer all of these, and the answers extend beyond choosing a platform. Questions like these turn a technology program into an exercise in institutional accountability, which also explains why such programs call for such a broad bench of professional expertise.
That breadth is something Deloitte has been building for a long time. The firm traces its uninterrupted Middle East presence back to 1926, and its regional offering now runs from audit and controls assurance to cyber, engineering, AI and data, alongside risk, regulatory and forensic services. The connection between those disciplines matters: the way a change in systems can alter what an organization needs to oversee, document and test.

Entrepreneur Middle East Staff
Entrepreneur Staff